> For the complete documentation index, see [llms.txt](https://docs.devolutions.net/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.devolutions.net/rdm/fr/knowledge-base/how-to-articles/configure-sql-server-for-protected-users-with-integrated-security.md).
# Configurer SQL Server pour les utilisateurs protégés avec la sécurité intégrée
Configurez les SPN de SQL Server pour l'authentification Kerberos afin que les Protected Users puissent se connecter par la sécurité intégrée de Remote Desktop Manager.
Voici les étapes pour configurer votre SQL Server afin de permettre à vos ***Protected Users*** de se connecter à la base de données à l'aide de la méthode d'authentification par sécurité intégrée.
Selon Microsoft, ***Protected Users*** bloque l'utilisation des [hachages NTLM](https://docs.microsoft.com/en-us/windows-server/security/credentials-protection-and-management/protected-users-security-group#domain-controller-protections-for-protected-users). Il est toutefois possible de configurer SQL Server pour qu'il utilise également [Kerberos pour la sécurité intégrée](https://docs.microsoft.com/en-us/sql/database-engine/configure-windows/register-a-service-principal-name-for-kerberos-connections). Ceci est pris en charge d'emblée par Remote Desktop Manager.
Pour que SQL Server prenne en charge l'authentification Kerberos, des SPN doivent être créés. Par défaut, le service s'exécute sous des comptes qui n'ont pas les permissions requises. Vous pourriez obtenir les messages suivants au démarrage de SQL Server (vous pouvez consulter les journaux dans SSMS sous ***Management SQL Server Logs***) : "The SQL Server Network Interface library could not register the Service Principal Name (SPN) for the SQL Server service."
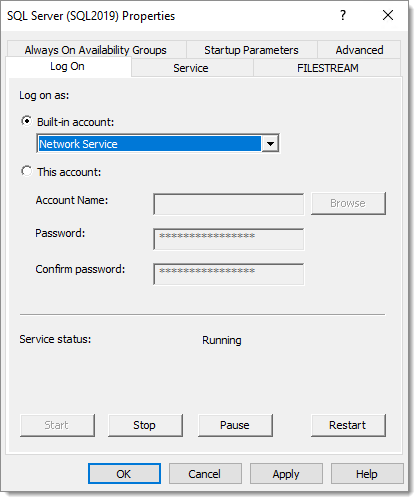
Vous devrez configurer le service SQL Server pour qu'il s'exécute sous ***Network Service***, car celui-ci possède les [permissions nécessaires](https://docs.microsoft.com/en-us/sql/database-engine/configure-windows/register-a-service-principal-name-for-kerberos-connections?view=sql-server-ver15#Permissions). Selon [cet article](https://dba.stackexchange.com/questions/180064/what-should-my-spn-entries-look-like-for-each-sql-instance/180147#180147), il est aussi possible d'accorder les permissions de créer des SPN à un compte de service. Vous devrez également changer le compte dans SQL Server Configuration Manager.
Cependant, SQL Server pourrait encore signaler qu'il n'a pas pu enregistrer les SPN. [Microsoft Kerberos Configuration Manager for SQL Server](https://www.microsoft.com/en-ca/download/details.aspx?id=39046) peut être utilisé pour corriger les SPN. Il affiche des boutons cliquables dans les colonnes Action.
Après le redémarrage du service SQL Server, vous devriez voir « The SQL Server Network Interface library successfully registered the Service Principal Name (SPN) \[ **MSSQLSvc/vdownsrv-sql3.downhill.loc:1433** ] for the SQL Server service. » dans les journaux.
À ce stade, la connexion devrait fonctionner de nouveau dans Remote Desktop Manager.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation dynamically by asking a question.
Perform an HTTP GET request on the current page URL with the `ask` query parameter, and the optional `goal` query parameter:
```
GET https://docs.devolutions.net/rdm/fr/knowledge-base/how-to-articles/configure-sql-server-for-protected-users-with-integrated-security.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is optional and describes the broader end goal you are ultimately trying to accomplish on behalf of the user. GitBook uses it to tailor the answer towards what is most useful for that goal.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.